A growing target on the road
AI data center construction is creating a lucrative target on US highways. Industry sources told NBC News that more than $100 million in data center freight has reportedly been stolen since June, with two recent attacks involving security vehicles and shipments worth millions. The reported total points to a problem that reaches beyond a single truck or site: valuable equipment has to travel through ordinary freight networks before it can be installed. That creates exposure at a stage when the cargo is concentrated, mobile and potentially difficult to replace quickly.
The figures also need careful reading. The article reports a source estimate, not a complete public accounting of every theft, and the incidents described don’t establish how often armed or collision-based attacks are occurring. Still, the cargo’s value and the reported tactics make this more significant than it might look at first. The thefts suggest that criminals are paying attention to what data center construction requires, not just to finished technology products.
High-value loads, direct attacks
In one case, a vehicle rammed a security escort accompanying a shipment of server equipment worth $13 million on an interstate route through California’s Mojave Desert. The trailer was later found at a truck yard without its cargo. The sequence suggests that the thieves were focused on taking the equipment, rather than simply stealing a vehicle or opportunistically stripping a load after a routine stop. But the details provided don’t establish how the cargo was tracked or how the thieves knew what the truck was carrying.
Gerado Pachucha, a former member of the Los Angeles County Sheriff’s Department cargo criminal apprehension team, told NBC the collision was deliberate: “The bad guys wanted that load, so they intentionally took out the escorts.” His assessment points to a practical weakness in relying on escorts alone: protection can deter an attack, but it can’t make a high-value shipment impossible to reach. An escort’s presence may also signal that the load is valuable, even if it doesn’t reveal what’s inside.
A second collision led to the theft of a trailer carrying an estimated $10 million in server rack components. Keith Lewis, who leads operations for Verisk CargoNet’s cargo theft tracking team, compared the shipments to “pure gold bars.” He said some individual loads have been valued at more than $30 million, adding: “It’s so much easier to steal this than to rob a bank.” The comparison is blunt, but it captures the appeal: a truck can carry a large amount of valuable, resalable equipment through routes where it may be exposed to theft. That doesn’t mean every component is easy to sell or that thieves can turn a stolen shipment into cash without difficulty.
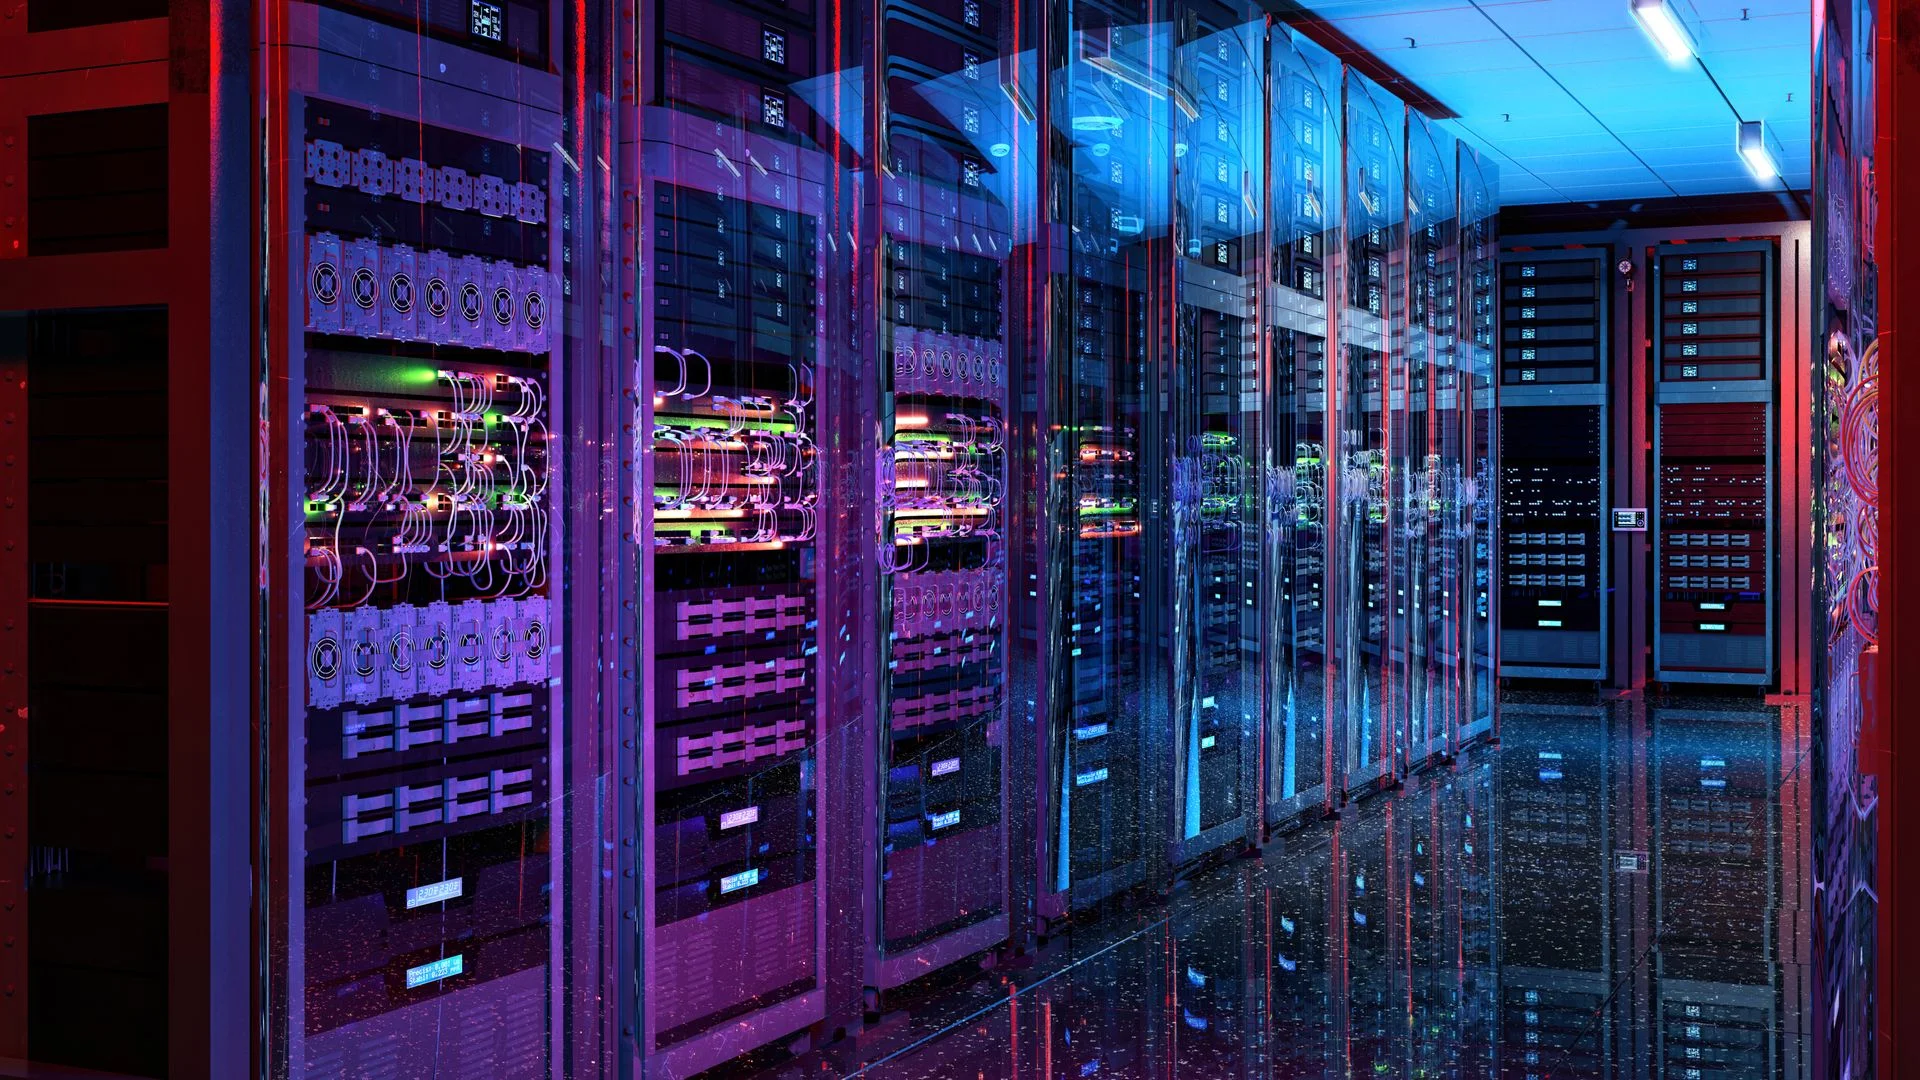
The equipment moving to data center sites includes server racks, RAM, storage drives, copper wire and fiber optic cable. Lewis said thefts are rising for components used early in data center construction, including copper, racks and memory. Their high price is drawing attention from cargo thieves. The range matters: a shipment doesn’t have to consist of finished servers to be valuable, and equipment needed at different stages of construction can become a target as it moves between suppliers, warehouses and sites.
That creates a supply chain problem with more than one vulnerable point. A missing load can mean the direct cost of replacing the goods, but a delayed delivery can also disrupt work that depends on those parts arriving in sequence. The source doesn’t quantify those knock-on effects, so their scale remains unclear. Even so, the basic pressure is plain: the more valuable components a project needs, the more attention logistics providers must pay to how those components are moved.
Organized methods and shifting risk
Physical attacks are only one part of the problem. In April, the FBI warned about “cyber-enabled strategic cargo theft,” describing schemes in which criminals impersonate freight brokers by spoofing email addresses, gain access to cargo systems and bid on shipments. Loads may then be redirected through complicit drivers under the pretext of being cross-docked or transloaded, before being moved elsewhere for resale. In these schemes, the theft can begin with false identities and access to shipping information, long before anyone approaches a truck on the road.
The two attacks on escorted shipments appear to be isolated in their method for now. But experts who spoke with NBC see them as a possible escalation toward more violent tactics used in other countries. Scott Cornell, chair of the Transported Asset Protection Association’s Americas division, described the crews as organized rings operating from a dozen countries and targeting freight across the US supply chain. “They’re planned. They’re plotted. They’re strategic. They’re playing chess in the supply chain,” he said. That description suggests that cargo security has to account for planning and deception as well as physical access. A guard at one point in the journey can’t, by itself, address every way a shipment might be identified, redirected or taken.
Arizona, California, Tennessee and Illinois have set up cargo theft task forces, while security escort firms are seeing more demand from data center logistics providers. Those responses show that the risk is drawing attention from both public agencies and the freight businesses handling these shipments. They don’t, on their own, show whether thefts are being prevented or recovered at a higher rate; the article provides no such outcome figures.
The attacks also highlight a broader supply chain exposure: the same organized crews may pursue other high-value freight as data center construction expands and more equipment travels across the country. If you’re working in this space, the practical issue is how to protect a shipment across its full journey, including the information and handoffs that can expose it. (And this is the part most people overlook.) The route, the records and the people arranging a load can matter as much as the truck carrying it.
What the incidents could mean for logistics
More demand for escorts may be one visible response, but the accounts here point to a wider set of weak points. A cargo operation depends on accurate shipment details, trusted brokers, reliable drivers and controlled transfers between carriers or facilities. Similar freight systems typically involve multiple companies and handoffs, which can make it harder to see who has access to information or who’s responsible at any given point. That complexity doesn’t prove a particular weakness caused these thefts; it does help explain why a single security measure may not cover the whole journey.
And yet, the evidence described so far leaves important questions open. The reported attacks involved very valuable loads, but the article doesn’t say how often similar shipments are targeted, how much stolen equipment is recovered, or whether the physical attacks are becoming more common. The difference matters: two dramatic incidents can reveal a real exposure without establishing a broad trend in tactics. Here’s the thing: the available details are enough to show why freight operators are paying attention, but not enough to predict how the threat will develop.
For data center builders, the immediate significance is straightforward. Construction depends on a flow of components that can be costly and time-sensitive, and those components are moving through a supply chain that criminals may already know how to exploit. More cargo on the road could create more opportunities for theft, though the source doesn’t establish how that risk will change as projects expand. The equipment is valuable. The routes are exposed. And the security response is still taking shape.